On this page
- What Is the TCPA and Why It Still Matters in 2026
- Why TCPA Compliance Is a Bigger Risk Than Most Businesses Assume
- The Real Cost of a TCPA Violation
- Core Rules Every Outbound Program Must Follow
- Building TCPA Compliance Into an Outsourced Call Center Program
- How Abacus BPO Approaches Compliance in Outbound Programs
- The Bottom Line
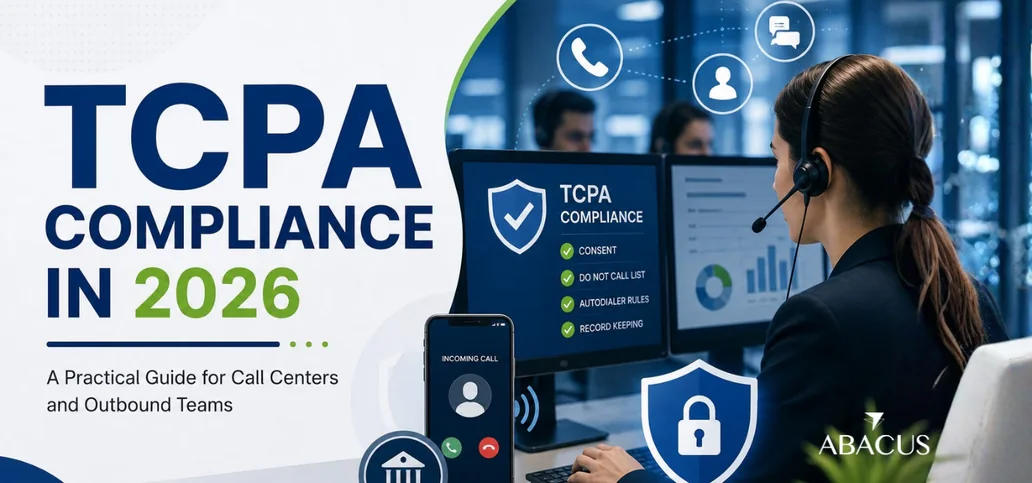
A single outbound campaign sent to an uncleaned contact list can turn into a multimillion-dollar liability overnight. That is not an exaggeration. TCPA litigation hit an all-time high in 2024, with 2,788 cases filed, a 112% jump from the year before, and average settlements now exceed $6.6 million. For any business running outbound calls or SMS in the United States, understanding the current rules is no longer optional.
This guide covers what the Telephone Consumer Protection Act actually requires in 2026, what violations really cost, and how outsourced call center programs stay compliant while still hitting outreach targets. At Abacus BPO, compliance sits inside every outbound program we run, so this is written from an operational standpoint, not just a legal summary.
What Is the TCPA and Why It Still Matters in 2026
The Telephone Consumer Protection Act was enacted in 1991 to restrict unsolicited telemarketing calls, autodialed calls, prerecorded messages, and text messages sent to mobile numbers without proper consent. It is enforced by the FCC and, just as importantly, it allows individual consumers to sue directly. That private right of action is what makes the TCPA one of the most litigated consumer protection statutes in the country.
The law operates under a strict liability standard. Intent does not matter. A misdialed call made in good faith carries the same penalty as one made recklessly, which is why compliance has to be built into systems and processes rather than left to agent training alone.
Why TCPA Compliance Is a Bigger Risk Than Most Businesses Assume
Several things have changed the risk profile heading into 2026:
- Phone number reassignment: Tens of millions of numbers are reassigned every year in the United States. A contact list that is six months old can already contain 3 to 5 percent reassigned numbers, and since consent follows the person, not the number, calling a reassigned line without fresh consent is a violation regardless of good intent.
- State-level "mini-TCPAs." States including Florida, Oklahoma, and Washington have enacted their own telemarketing laws with stricter consent rules and shorter calling windows than the federal statute. Florida alone accounts for roughly 7 percent of the US population, so a single misconfigured dialer setting can create exposure on top of federal penalties.
- AI voice calls now count: The FCC's 2024 declaratory ruling confirmed that AI-generated voices qualify as "artificial voices" under the TCPA, meaning AI-powered outbound calling carries the exact same consent obligations as a traditional autodialer.
- Recordkeeping requirements tightened: Under the amended Telemarketing Sales Rule, businesses must now keep detailed records of every individual telemarketing call, including the script used and the call disposition, for five years instead of two.
The Real Cost of a TCPA Violation
| Violation Type | Penalty Range | Additional Detail |
|---|---|---|
| Non-willful violation | $500 per call or text | Set by statute, 47 U.S. Code Section 227(b)(3)(B) |
| Willful or knowing violation | Up to $1,500 per call or text | Courts determine willfulness case by case |
| Do Not Call Registry violation | Up to $43,792 per call | Stacks on top of standard TCPA statutory damages |
| Class action exposure | No statutory cap | A single flawed campaign to a large list can produce millions in liability |
| Average TCPA settlement (recent data) | Exceeds $6.6 million | Reflects rising litigation activity and larger class sizes |
| TCPA lawsuits filed in 2024 | 2,788 cases | A 112% increase over the prior year |
| Telemarketing Sales Rule recordkeeping requirement | 5 years per call record | Increased from 2 years under the amended TSR |
The number that catches most businesses off guard is not the per-call fine. It is that figure multiplied across an entire contact list. A campaign sent to 50,000 numbers without proper consent is not one violation. It is potentially 50,000.
Core Rules Every Outbound Program Must Follow
Regardless of company size or industry, a compliant outbound program needs to consistently handle the following:
- Prior express written consent: Required before using an autodialer or prerecorded message to call or text a mobile number, and the consent must be specific, documented, and not bundled as a condition of purchase.
- Calling window enforcement: Calls to residential and mobile numbers are restricted to 8:00 AM to 9:00 PM in the recipient's time zone, not the caller's.
- Do Not Call scrubbing: Every outbound list must be checked against the National DNC Registry and the business's own internal do-not-contact list before dialing.
- Opt-out processing: Opt-out requests should be acknowledged quickly (a five-minute confirmation window is considered best practice) and honored across every communication channel, not just the one the request came through.
- Fresh data hygiene: Contact lists need regular scrubbing against reassigned-number databases, since stale data is one of the fastest ways to trigger accidental violations.
- Full call documentation: Under the amended TSR, each call record should include the numbers involved, date, time, duration, script used, and disposition, retained for five years.
A lack of documented consent remains the single leading cause of TCPA lawsuits, which makes recordkeeping just as important as the consent itself.
Building TCPA Compliance Into an Outsourced Call Center Program
Here is the part many businesses overlook: if an outsourced call center makes a non-compliant call on your behalf, the liability generally falls on your company, not the vendor. Entities can be held vicariously liable for TCPA violations committed by agents they hired to run their calling campaigns, even when they did not personally place the call. That makes vendor due diligence part of TCPA compliance itself, not a separate step.
Before handing outbound campaigns to any BPO partner, it's worth confirming:
- How they capture and store proof of consent for every contact
- Whether their dialing technology automatically enforces time-zone calling windows
- How frequently their contact data is scrubbed against DNC and reassigned-number databases
- Whether AI-assisted calling tools are held to the same consent standards as traditional autodialers
- What their record retention process looks like, and whether it meets the five-year TSR requirement
A vendor that cannot answer these clearly is a liability wearing a service agreement.
How Abacus BPO Approaches Compliance in Outbound Programs
Our outbound operations are built around the same principle running through the data above: compliance has to be structural, not just procedural. In practice, that means:
- Consent documentation captured and stored at the point of contact, not reconstructed after the fact
- Automated DNC and time-zone scrubbing built into dialing workflows rather than left to manual review
- Regular contact list hygiene to reduce reassigned-number risk
- Full call-level recordkeeping aligned with current TSR retention requirements
Ongoing agent training that reflects the latest FCC guidance, since the rules have shifted multiple times in the past two years alone
The Bottom Line
TCPA compliance is not a one-time checklist. It is an ongoing operational discipline that touches consent capture, data hygiene, calling technology, and recordkeeping all at once. With litigation volume up sharply and per-violation fines uncapped in class actions, the cost of treating compliance as an afterthought has never been higher. Whether outbound programs are run in-house or through an outsourced partner, the businesses that stay protected are the ones that build compliance into the infrastructure itself, not just the training manual.